Critical PHP vulnerabilities disclosed; OpenAI says its models found them; NSA issues advisory
OpenAI says models under its Patch the Planet initiative helped researchers find critical PHP flaws, with a two-month coalition preparing fixes before disclosure. Greg Brockman says more bugs are coming, including a Node.js RCE. The NSA issued an emergency advisory; Samuel Hammond shared context on scale. Some posts call risks to ~70% of PHP sites severe.
All posts · 9, most important first
- OpenAI models helped researchers—operating as part of our Patch the Planet initiative—discover critical security flaws in PHP, an open-source programming language used to run an estimated 70% of websites. Over the past two months, we led a coalition of maintainers, researchers, and security providers to prepare fixes and protections ahead of disclosure. This duration was necessary because the fix was quite intricate and required a major change to the PHP engine. Every site using PHP can now safely upgrade their version to stay secure, in addition to applying mitigations from various security vendors. Due to the severity of these flaws and PHP’s widespread use, we consider this bug to be one of the most impactful vulnerabilities in recent memory. It also marks a new phase, where AI can find security bugs with internet-scale impact. This is an example of the Defender’s Window in action: to our knowledge, frontier AI was able to find this vulnerability ahead of attackers, giving defenders time to prepare. openai.com/index/coordina…1,619 likes · 438 reposts
- Greg Brockman: 'We have been in parallel working on fixing several other significant bugs we've found, including a remote code execution that Node.js announced today, but with less collective attention due to bandwidth constraints across our team and partner organizations. We expect to find many more such issues over upcoming months.'
 Over the past two months, we have been leading a coalition to mitigate one of the most severe bugs in open source software found in recent memory, php2shell, found as part of our Patch the Planet initiative. https://t.co/rBsz7lrlwo open on X24 likes · 1 reposts
- Rare NSA post:Effective Immediately, all organizations using PHP for their systems are advised to be prepared for an update addressing two critical vulnerabilities. PHP is widely used for web applications. These vulnerabilities often provide a direct path to the server's file system or database. If an immediate update is not feasible, it is recommend that organizations take the system offline until it can be fully mitigated. NSA will follow up shortly with more specific guidance. open on X10 likes · 0 reposts
- unfortunately just saying it exists is very likely enough to result in people finding it within hours4 likes · 0 reposts
- Context on what "massive" means
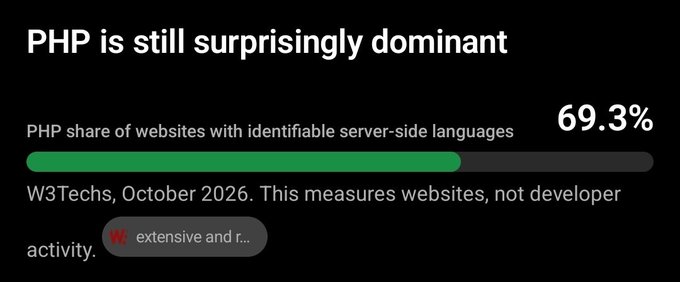 🚨 A MASSIVE internet security emergency is unfolding right now. 🚨 Two CRITICAL vulnerabilities have been discovered in PHP, potentially putting millions of websites at risk. → NEARLY 70% of websites with a known server-side language run PHP. The potential scale is ENORMOUS. → TWO CRITICAL security flaws have been confirmed, each scoring 9.2/10 in severity. → Attackers could potentially take control of vulnerable servers remotely, without authentication. → Reports suggest PHP versions dating back to 2004 could be affected. The exact scope is still unconfirmed. → EMERGENCY PATCHES are scheduled for TOMORROW at 10 AM ET. Website owners are being urged to prepare immediately. → Europe's CERT-EU is warning organizations to patch ASAP or consider TAKING EXPOSED APPLICATIONS OFFLINE if they cannot be secured. → WordPress, Magento, Laravel and potentially millions of other PHP-powered websites could be at risk. → Once patches go public, hackers could reverse-engineer them and race to attack servers that haven't updated. The vulnerabilities are CONFIRMED. The full technical details remain secret. Tomorrow, the race between hackers and defenders begins. This could get ugly. FAST. open on X2 likes · 1 reposts
- From OAI:Largest credit goes to @lcfr_hax for the earliest recent discovery of the bug class. This underlying engine issue was so wide it invited a lot of parallel discovery. As we coordinated our findings the scope of the problem continued to expand! open on X5 likes · 0 reposts
- OpenAI says the PHP security flaw (found with GPT-5.6 Sol) is the tip of the iceberg, and they have several more discoveries to announce.
 @openai: OpenAI models helped researchers—operating as part of our Patch the Planet initiative—discover critical security flaws in PHP, an open-source programming language used to run an estimated 70% of websites. Over the past two months, we led a coalition of maintainers, researchers, and security providers to prepare fixes and protections ahead of disclosure. This duration was necessary because the fix was quite intricate and required a major change to the PHP engine. Every site using PHP can now safely upgrade their version to stay secure, in addition to applying mitigations from various security vendors. Due to the severity of these flaws and PHP’s widespread use, we consider this bug to be one of the most impactful vulnerabilities in recent memory. It also marks a new phase, where AI can find security bugs with internet-scale impact. This is an example of the Defender’s Window in action: to our knowledge, frontier AI was able to find this vulnerability ahead of attackers, giving defenders time to prepare. openai.com/index/coordina… open on X29 likes · 4 reposts
 🚨DEFCON 1🚨 In a few hours, a critical vulnerability that affects ~70% of web sites will be disclosed. It allows an attacker to upload and execute arbitrary code. It's probably best if you stop browsing the internet for the rest of the week. open on X2 likes · 0 reposts
- NSA:Effective Immediately, all organizations using PHP for their systems are advised to be prepared for an update addressing two critical vulnerabilities. PHP is widely used for web applications. These vulnerabilities often provide a direct path to the server's file system or database. If an immediate update is not feasible, it is recommend that organizations take the system offline until it can be fully mitigated. NSA will follow up shortly with more specific guidance. open on X1 likes · 0 reposts
 @openai org ·
 @andrewcurran_ commentary ·
 @tenobrus commentary ·
 @hamandcheese policy ·